Breach simulations built for regulated industries
Expert pentesting and realistic incident simulations that prepare your team for a real attack, with audit-ready evidence on demand.
Experts certified by
- Microsoft
- OffSec
- CompTIA
- PortSwigger
Instant CSIRT simulations
Train your incident response team in hours, not months
Launch a realistic DeepDive scenario, based on sector-relevant threat intelligence, whenever you need one. Built to challenge your leaders as much as your responders, it ends with an audit-ready report and a clear plan to strengthen your response.
Live, branching incident simulation
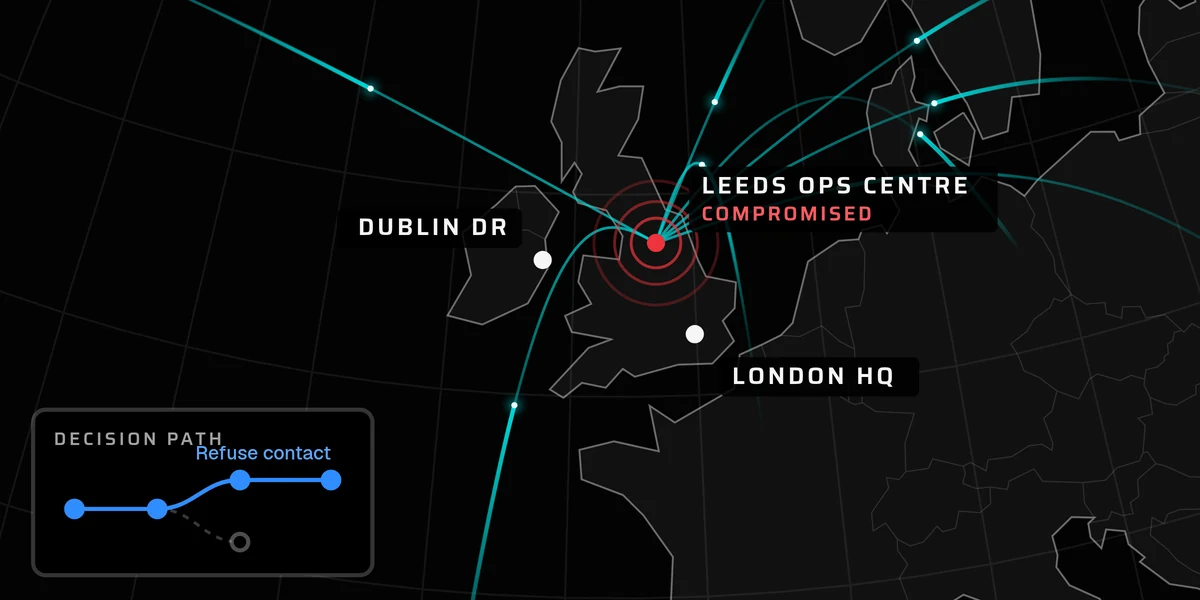
Fine-tuned simulation control
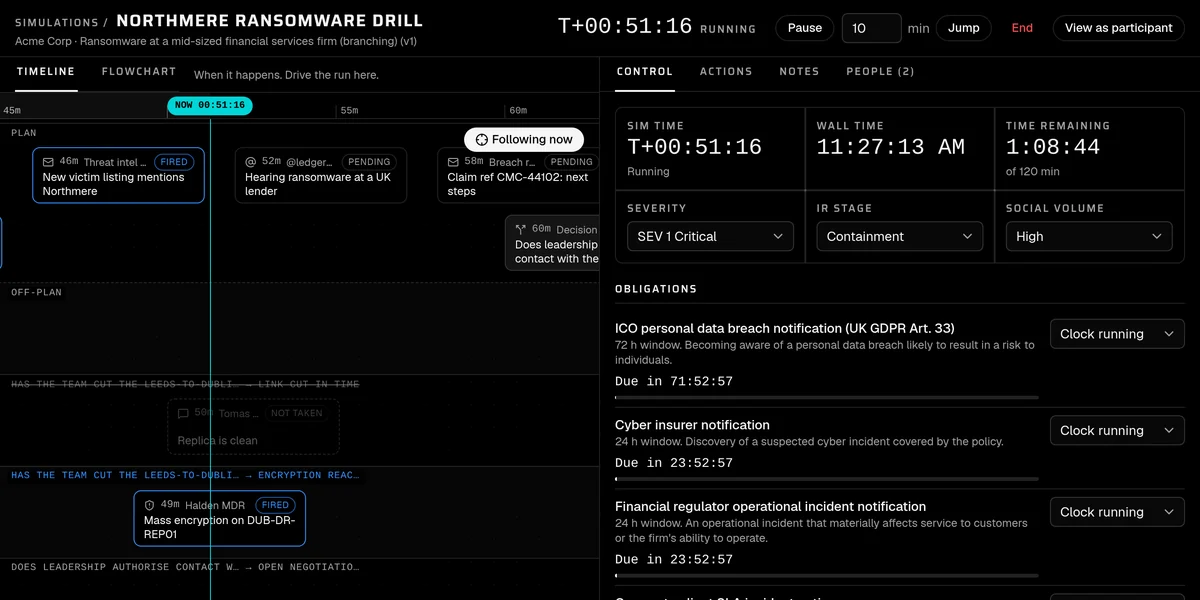
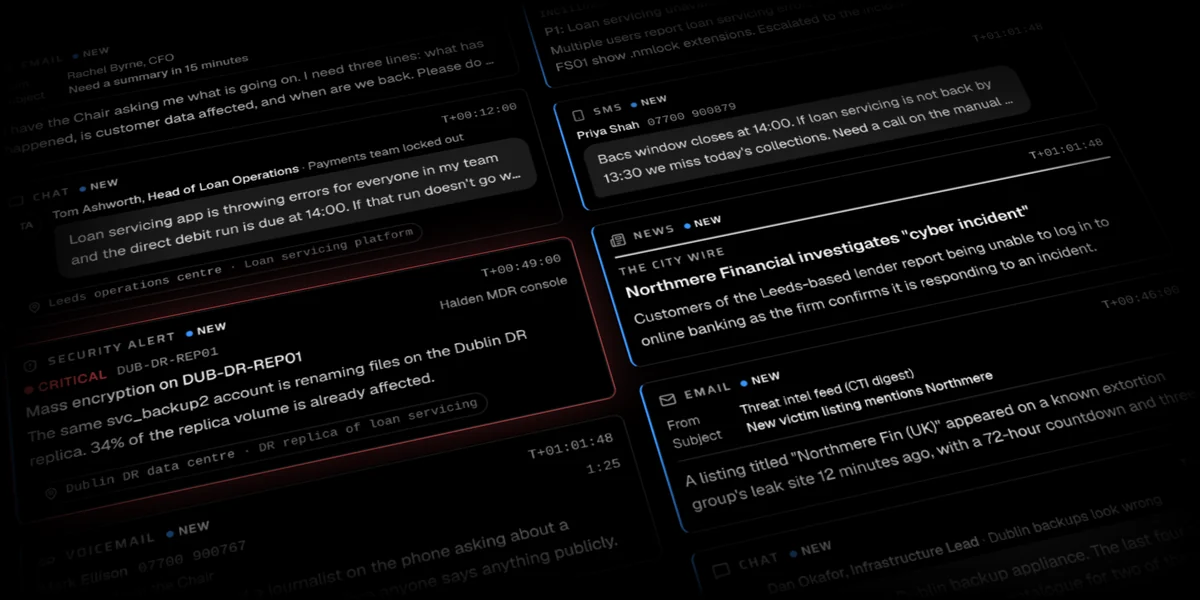
Realistic live injects
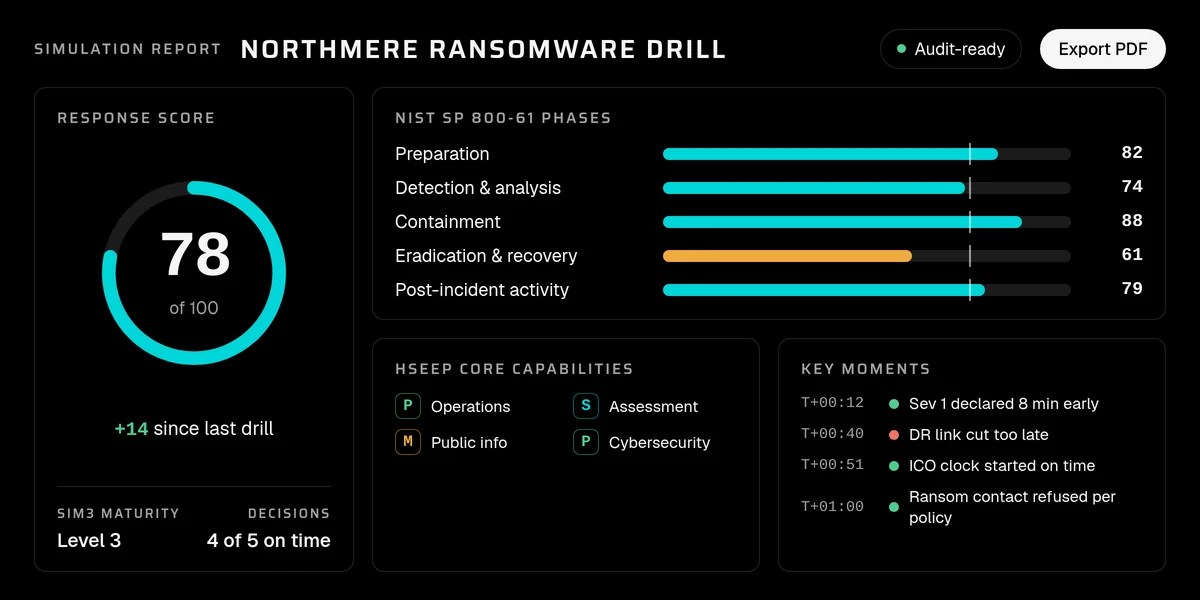
Deep, audit-ready insights
Launch in seconds
Choose a prebuilt scenario, such as ransomware, supply chain attacks or web defacement, and start instantly. Or, work with us to build you something custom.
Scenarios that bite
Branching injects that react to your team’s decisions, built by the same experts who run our pentests. Designed to expose gaps in your response, and help you fix them.
Audit-ready feedback
Every run is scored on a framework built on NIST, HSEEP and SIM3 guidelines, with actionable feedback and a tailored improvement strategy.
Our guarantee
Measurable improvement, guaranteed
Run DeepDive for 90 days and put our feedback into practice. If your team’s response scores haven’t improved from your first simulation, we’ll give you a year of access free.
Preparation
We evaluate your incident response plan, playbooks, and team preparation before a simulation even begins.
Detection & Analysis
Get a read on your team’s ability to investigate an incident, and their capacity to understand the root cause of cybersecurity breaches.
Containment, Eradication & Recovery
Develop and assess your organisation’s ability to apply practical incident response measures to close an incident.
Post-Incident Activity
Assess your incident management, team communication, and ability to apply feedback to improve your response.
Continuous pentesting
Continuous pentesting, with experts in your corner
DeepDive turns pentesting from a shallow, one-off snapshot into a continuous process with free retesting. Security that works with your business, not against it.
Pentests, not PDFs
Continuous testing that grows with your business, plus a live dashboard and tracking support to help your team close its backlog.
Direct line to an expert
Get direct support from OSCP-certified professionals, with no barrier between you and the expertise.
Remediation support
We help you fix what we find, then retest for free to confirm it’s closed, so findings don’t sit until next year’s audit.
What sets us apart
A system, not a pentest
| What most pentests leave behind | What we leave you with |
|---|---|
| A PDF that’s out of date by the next release | Continuous testing that keeps pace as you ship |
| Account managers between you and the tester | A direct line to the OSCP-certified expert testing your systems |
| A growing backlog of findings with no ownership | Hands-on remediation support and guidance |
| Retests billed as a new engagement | Free retesting |
| Scattered information for executive and audit reporting | Clear trends and remediation metrics for executives and auditors |
Hear it from them
Trusted security for regulated industries

“Security findings were reported with sufficient technical detail for our engineers to act on directly, and prioritised in a way that let us focus remediation effort where it mattered most.”
Naudé MullerCTO, IDToday Secure Data Solutions 
“The content delivered was of a high standard, relevant and engaging. The Aphotic Security team demonstrated professionalism, efficiency and a clear commitment to delivering meaningful value to participants.”
Mufaro NesonganoExecutive, Communications Regulatory Authority of Namibia 
“The team demonstrated a strong ability to translate cybersecurity and incident-response theory into practical and workable solutions that organisations can adopt and implement within their local operating environments.”
Paulinus SheehamaChairman, DSTech Namibia
The stakes
Data breaches can sink your business
The impact of a breach goes far beyond data compromise. It can grind your operations to a halt. But the real loss is much harder to reverse: damaged customer trust, regulatory fines and a reputation that takes years to rebuild.
- Global average cost of a data breach — the highest in the study’s history
- $4.99M
- IBM Cost of a Data Breach Report, 2026
- Of breaches involved a third party, up from 30% the year before
- 48%
- Verizon Data Breach Investigations Report, 2026
- Average time to identify a breach, with 64 more days to contain it
- 183 days
- IBM Cost of a Data Breach Report, 2026

Ready to dive deeper?
Get an expert read on your security in 30 minutes, and a clear plan for what to improve next.